Careful notes on Android packages, signing, delivery and the limits of technical evidence.
The APK review notebook: record claims and evidence in separate columns
A useful technical note makes clear what was observed and what was merely claimed. This small discipline prevents a package review from turning marketing…
Play Protect is one layer in an APK decision
Android’s app protection mechanisms are useful, but their presence should not become a reason to ignore where a package came from. A sound installation…
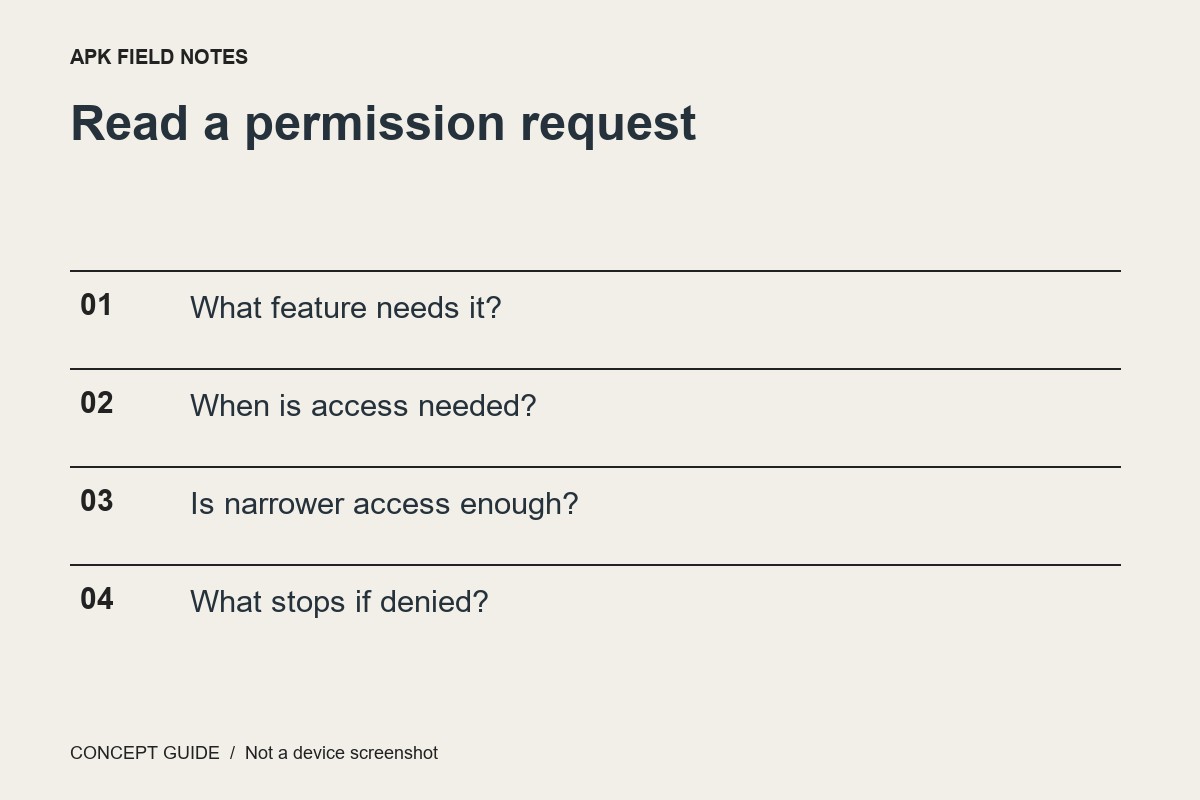
Read Android permissions in the context of one feature
A permission list is more useful when tied to the feature a reader intends to use. The same capability can be reasonable for one…
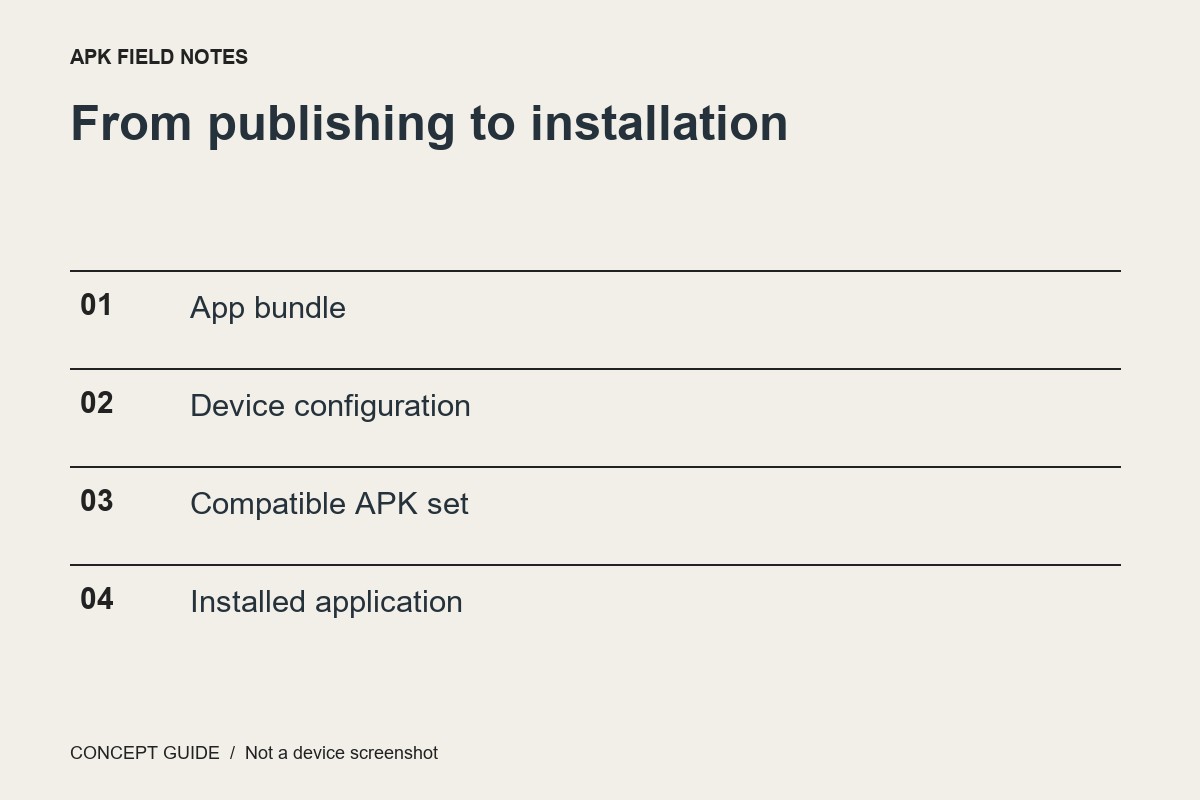
Why a split APK download may be incomplete
Some Android apps are installed from multiple APK components selected for a device. A download containing only one component may not represent a complete…
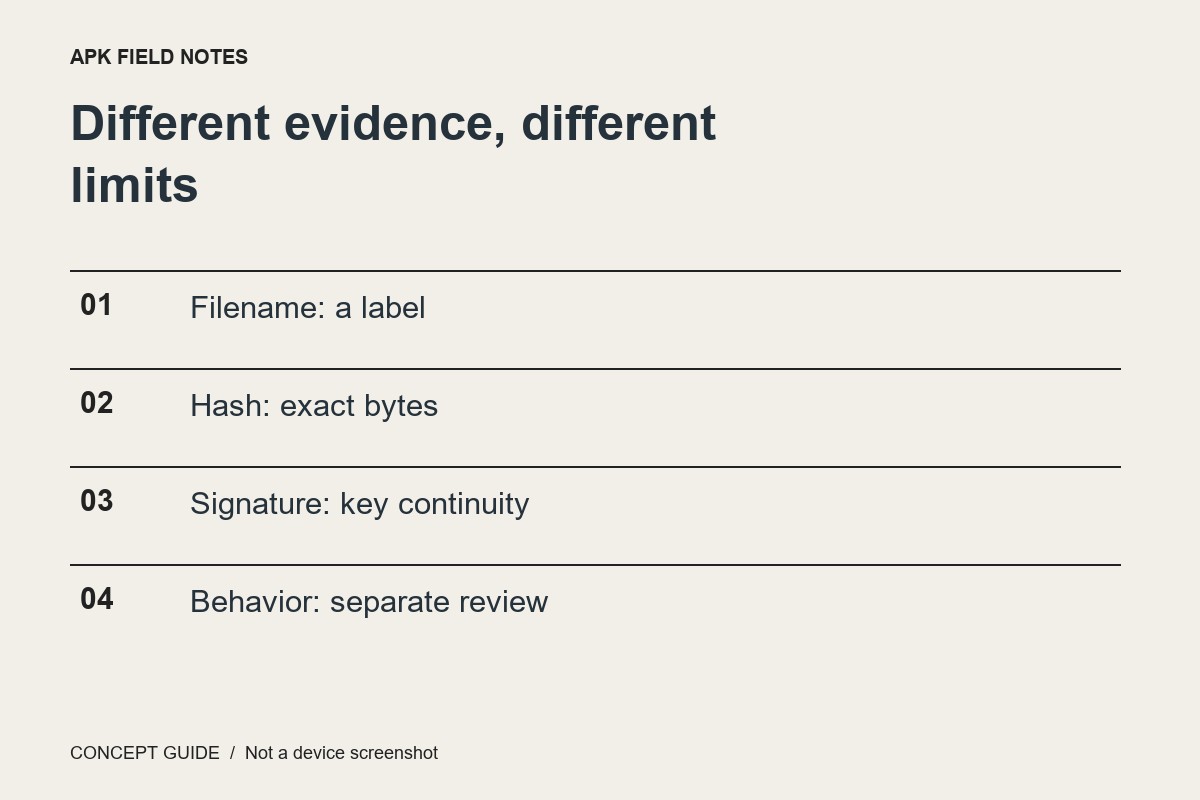
APK signing explained as continuity, not a trust badge
Android app signing helps connect a release to a signing identity and supports update relationships. It is important evidence, but a signature is not…
A hash identifies bytes; it does not certify an APK as safe
A checksum comparison can answer whether two files have the same contents under a particular hash algorithm. It cannot by itself establish who should…
APK, app bundle and installed app: three objects, three different jobs
Android discussions often use package as if it describes one thing. Separating the publishing artifact, the installable artifacts and the installed application makes many…